
Cloud infrastructure, DevOps & security
Environments that hold under load, and a route to production that anyone on the team can run.
The challenge
Every environment is a project
A new environment, brand or region should be routine. Instead it's weeks of tickets, hand-built configuration and differences nobody can explain. Security gets bolted on afterwards, and the cloud bill grows faster than the business. Now add the newest line item nobody budgeted for: AI workloads, tokens and GPUs, all unmetered.
Our approach
The foundation, defined as code
We define your cloud environments once, as code, with identity, networking, the security baseline and cost controls in from day one, so the next environment is a pipeline re-run, not a project. Costs get owners, budgets and automation. That includes AI spend, measured and governed like any other cost.
Results
A platform team that scales by code, not by clicking
Faster environment stand-up, a predictable security posture, and cost growth that tracks usage rather than experimentation accidents.
What we do
Reproducible infrastructure across dev, staging and prod. No "works on my subscription".
- Dev, staging and prod described in code, identical by construction
- Changes go through review; the environment's history is a git log
- A new environment is an afternoon, not a quarter
A route to production anyone on the team can run: tests and reviews on every change, environments promoted in order, and a release that is a routine event rather than a Friday no one enjoys. Data pipelines and models go through the same gates as application code, because they break the same way.
- Build, test and deploy on every change, with promotion through dev, UAT and production behind approvers
- Deployments repeatable and reversible, rather than tribal knowledge held by whoever did it last
- Data pipelines and models shipped under the same gates as the application
- A broken change caught in staging instead of by a customer
Identity, secrets, network isolation and hardening set up as part of the foundation, not bolted on after the incident. Designed to pass a security review, and the audit after it, the first time.
- Identity, secrets, network isolation and hardening in the foundation
- Least-privilege access as the default posture everywhere
- Designed to pass the security review, and the audit after it, the first time
Cost attribution per team and product, right-sizing and shutdown automation, plus the new line item nobody budgeted for: AI. Token spend, GPU workloads and model serving measured and governed like any other cost, before the invoice does it for you.
- Cost attribution per team and product, so every invoice line has an owner
- Right-sizing and shutdown automation on schedules that match real usage
- AI spend (tokens, GPU workloads, model serving) governed like any other cost
Proven in production
Web
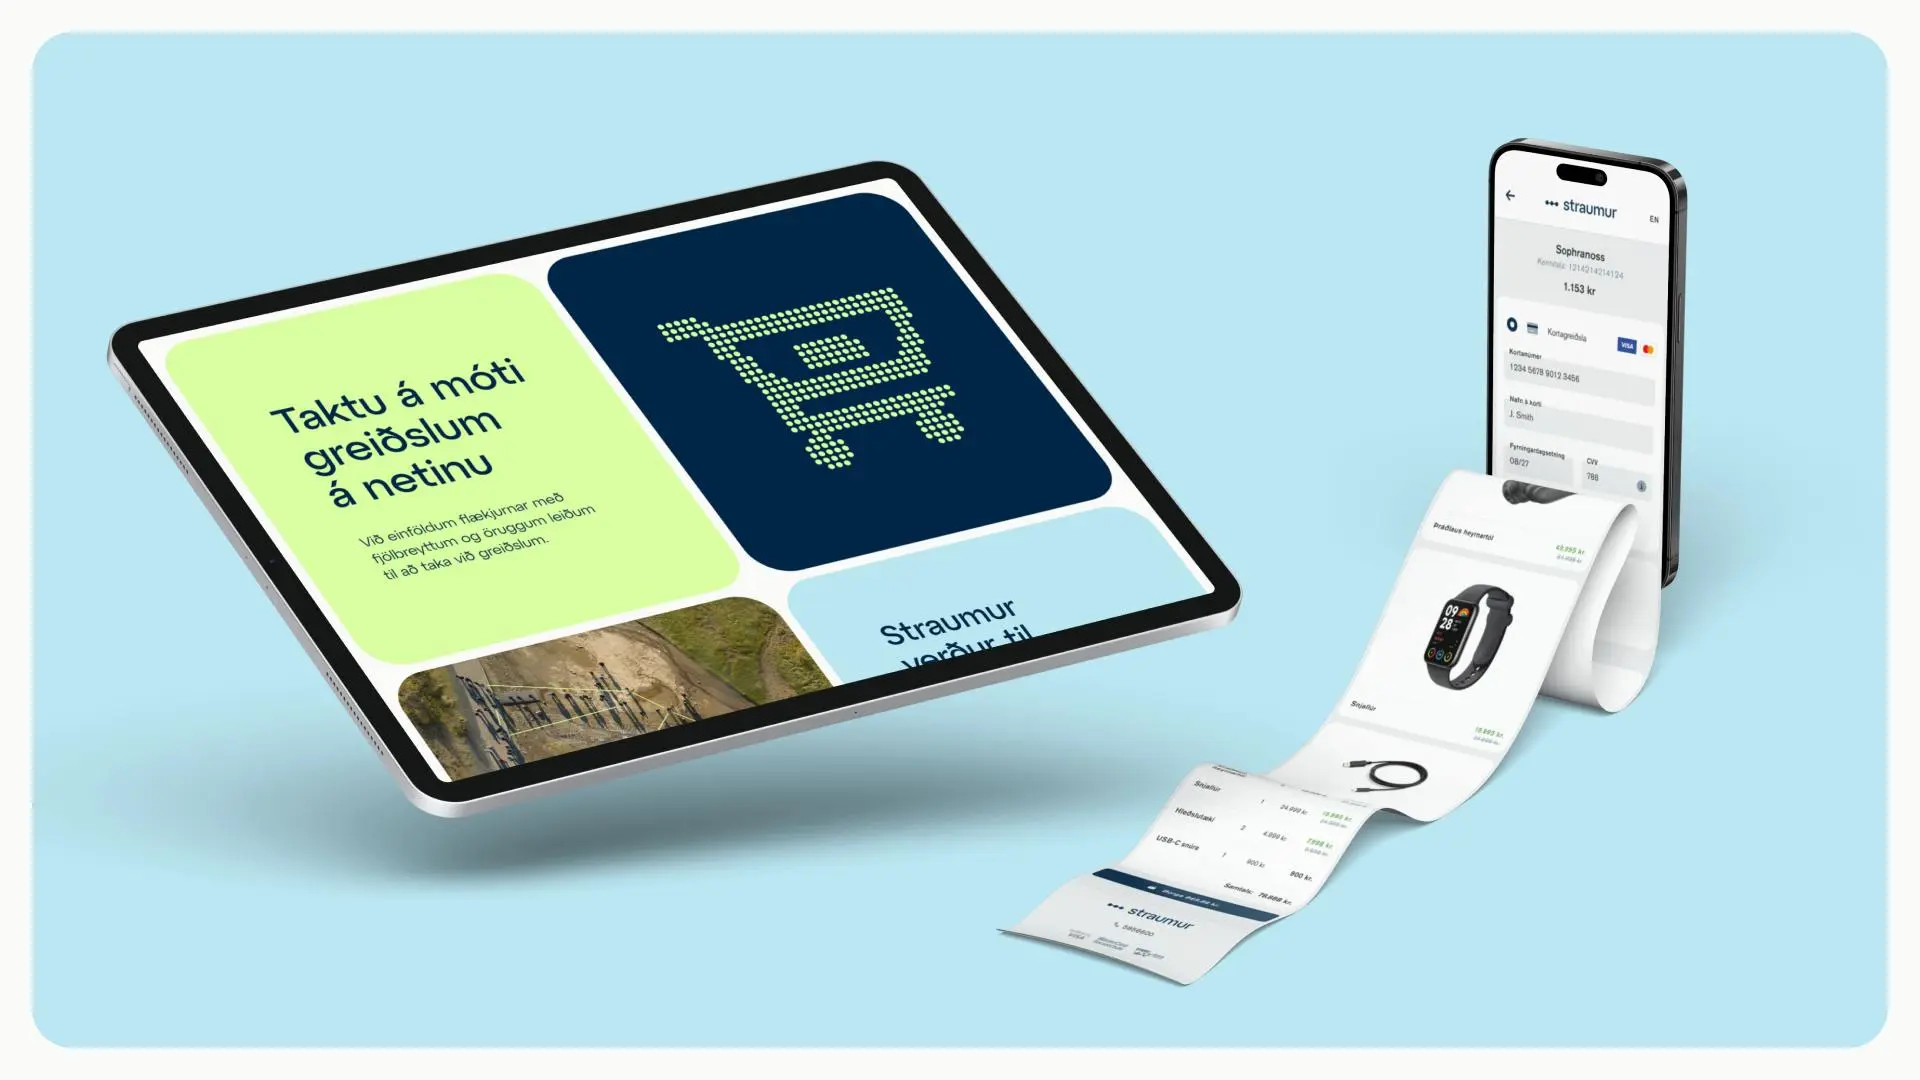
Straumur: A payment facilitator built from an empty repository
Onboarding, processing, settlement, portals and APIs, written from an empty repository. From kick-off to live money in about seven months, and 50M+ transactions in the first eighteen.
Web & Mobile
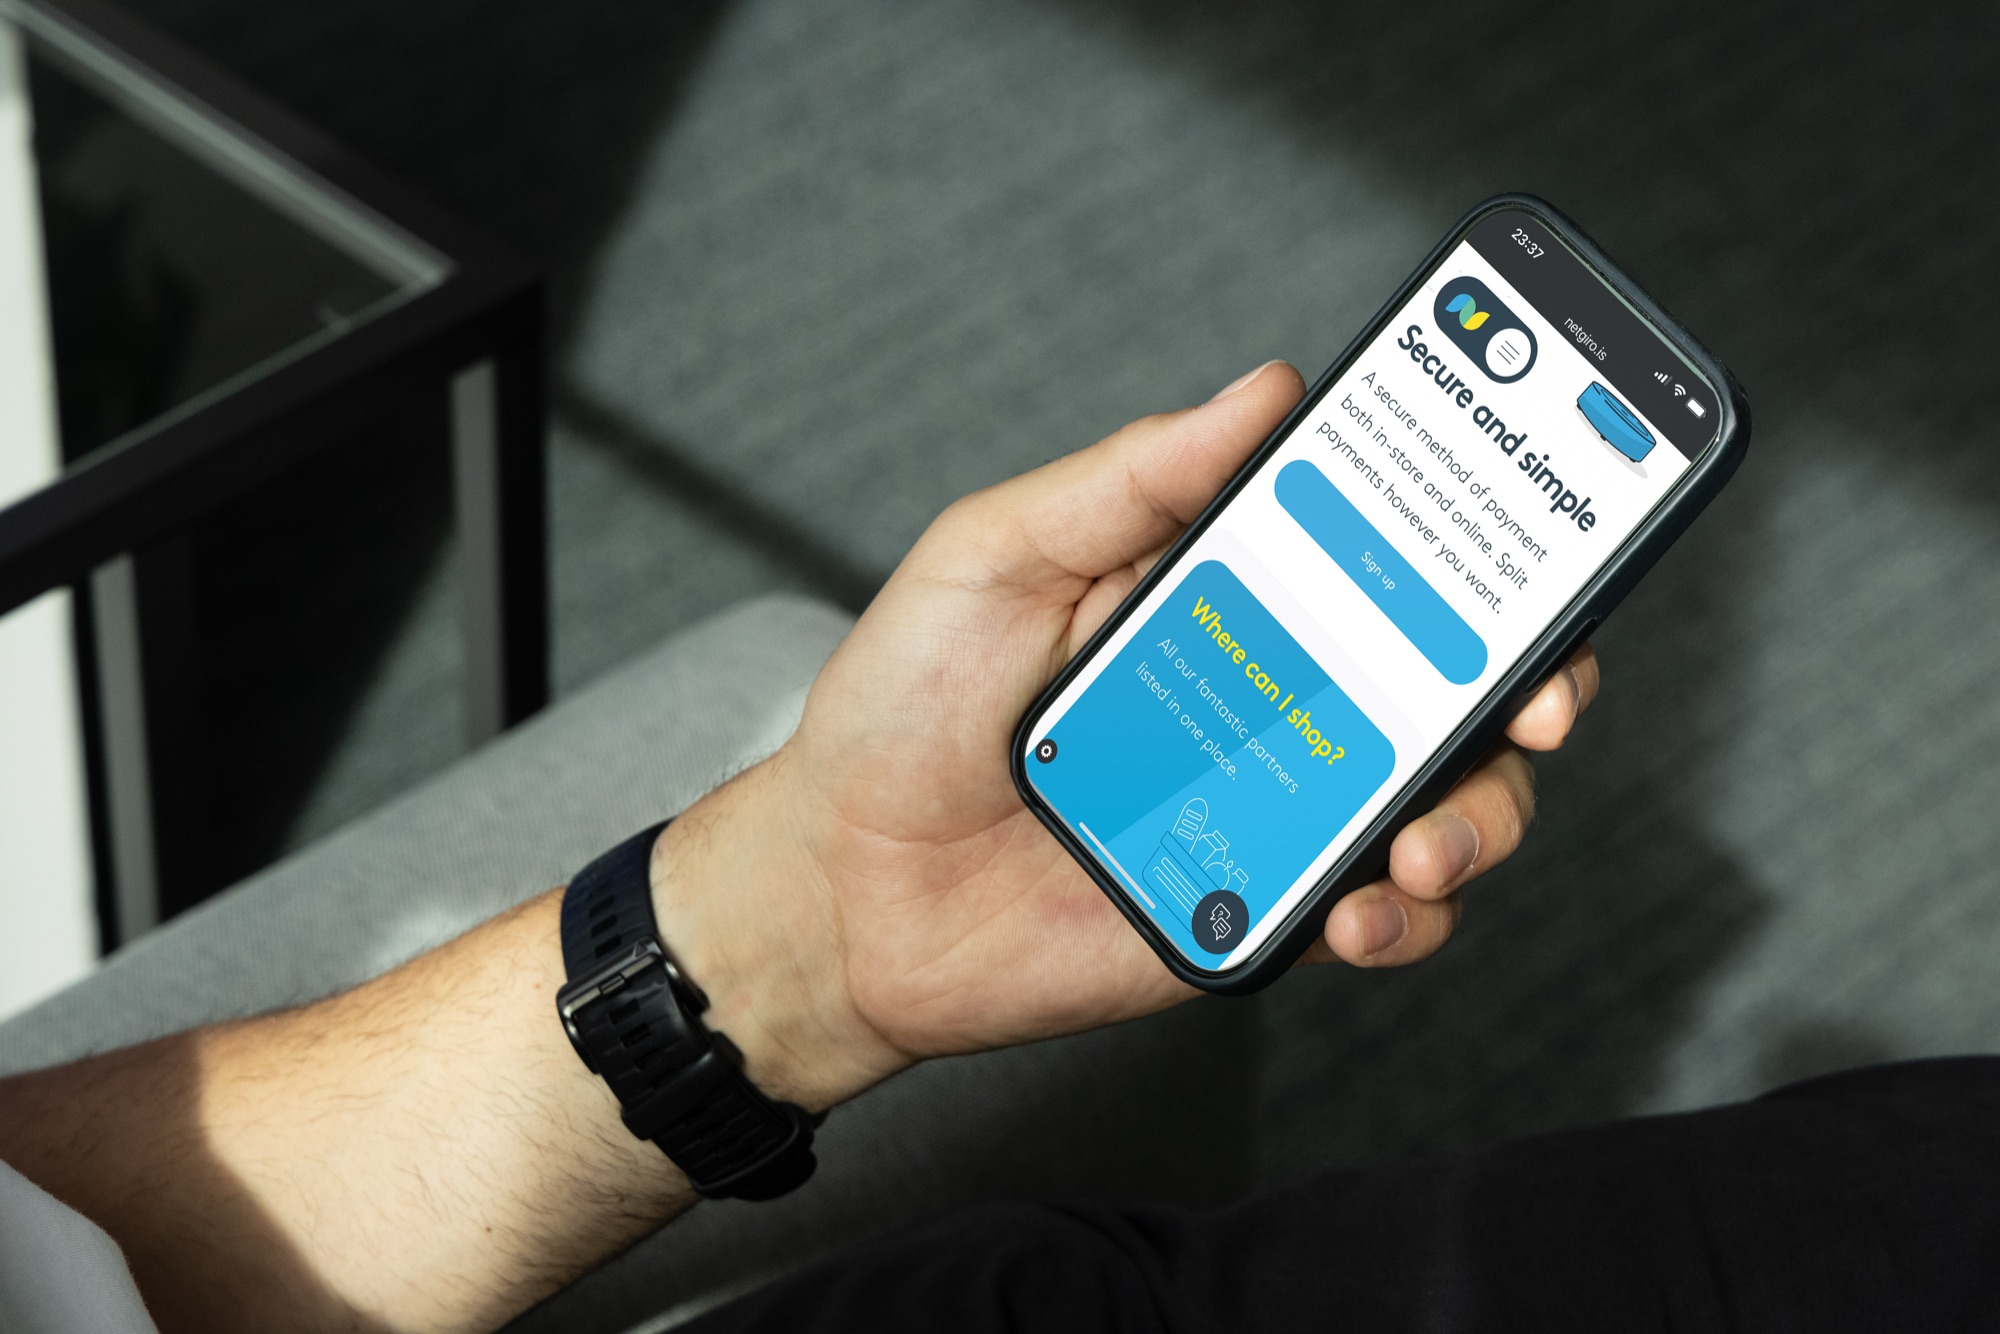
Netgíró: Iceland's national payment method
Iceland's leading buy now, pay later platform, built and scaled over more than a decade of partnership.
Web
Gaveia: One backend, four booking platforms
Four holiday booking platforms across Croatia and Slovenia, all standing on one core business system: the properties, the prices, the internal tools, and now the AI that answers travellers.